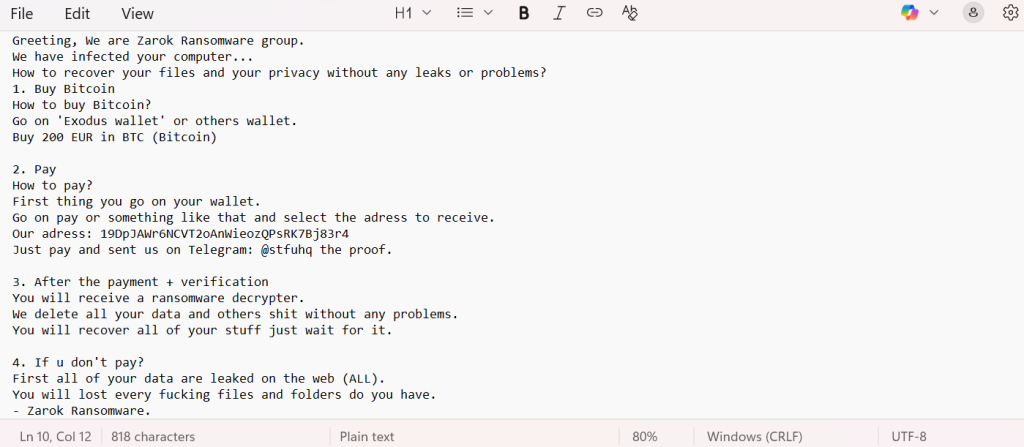
Zarok ransomware is a data-encrypting malware recently identified through submissions to VirusTotal. Once active, it encrypts files and appends a unique four-character random extension such as .ps8v to each filename. For instance, document.pdf becomes document.pdf.ps8v. After encrypting data, it replaces the victim’s desktop wallpaper and drops a ransom note titled “README_NOW_ZAROK.txt.”
The note demands payment of approximately €200 in Bitcoin, though the wallpaper message has mentioned sums as high as €500. Victims are directed to send proof of payment through Telegram (@stfuhq) in exchange for a decryptor tool. The attackers claim that, after verification, they will unlock files and delete stolen data — yet threaten public leaks for nonpayment.
Our incident response team has developed a controlled decryptor workflow specifically for Zarok infections. This process is built to ensure the safe recovery and preservation of encrypted assets through verified cryptographic analysis.
The decryptor framework:
Runs in a forensic sandbox to identify the exact Zarok build.
Extracts key fingerprints and variant markers based on file header patterns.
Performs PoC decryption tests to confirm key structure integrity before restoring data.
It supports both cloud-linked verification (for rapid analysis) and offline use in high-security environments. Every session begins with read-only validation to prevent corruption and preserve forensic traceability.
Disconnect all affected devices from local networks, storage arrays, and the internet.
Preserve encrypted files and ransom notes exactly as they appear — do not rename or modify them.
Collect evidence: firewall logs, system events, malware binaries, and email headers.
Capture system memory (RAM) if possible — active encryption keys or exfil traces may exist.
Avoid direct negotiation through Telegram or email; allow certified experts to handle communication.
Recovery Options
Standard / Free Routes
Offline or Immutable Backups — Restore from clean, pre-infection backups after verifying their integrity. Disconnect all infected systems before initiating the process.
No Free Decryptor (as of 2025) — While several Chaos-derived ransomware strains have been cracked, no verified decryptor currently exists for Zarok. Victims are encouraged to monitor No More Ransom for future releases.
Professional / Advanced Methods
Forensic Decryptor Service — Our team can safely analyze samples and attempt key reconstruction using cryptographic reverse-engineering. If PoC decryption is successful, we proceed with full restoration.
Ransom Payment (Not Recommended) — Paying the ransom may not guarantee recovery or data deletion. Cybercriminals often retain or resell stolen information even after payment.
How to Use Our Zarok Decryptor — Step-by-Step
Step 1: Verify infection — confirm that encrypted files end with random four-character extensions (e.g., .ps8v) and locate the ransom note README_NOW_ZAROK.txt.
Step 2: Secure your environment — isolate the affected system and ensure backups are offline.
Step 3: Contact our recovery team — provide encrypted samples and ransom materials for variant identification.
Step 4: Launch the decryptor as administrator — online connectivity may be required for key mapping.
Step 5: Input your unique Victim ID — found within the ransom note — to match your case data.
Step 6: Begin decryption — files will be restored to a clean folder with full integrity and recovery reports.
File Name: README_NOW_ZAROK.txt Location: Typically dropped in each directory with encrypted data.
Excerpt:
Greeting, We are Zarok Ransomware group. We have infected your computer… How to recover your files and your privacy without any leaks or problems?
1. Buy Bitcoin How to buy Bitcoin? Go on ‘Exodus wallet’ or others wallet. Buy 200 EUR in BTC (Bitcoin)
2. Pay How to pay? First thing you go on your wallet. Go on pay or something like that and select the adress to receive. Our adress: 19DpJAWr6NCVT2oAnWieozQPsRK7Bj83r4 Just pay and sent us on Telegram: @stfuhq the proof.
3. After the payment + verification You will receive a ransomware decrypter. We delete all your data and others shit without any problems. You will recover all of your stuff just wait for it.
4. If u don’t pay? First all of your data are leaked on the web (ALL). You will lost every fucking files and folders do you have.
Initial Access: Phishing emails, malicious torrents, or software cracks.
Execution: AES/RSA encryption and extension appending.
Persistence: Modifies registry keys for ransom-note display.
Defense Evasion: Deletes shadow copies and disables recovery.
Exfiltration: Transfers stolen data to attacker-controlled servers.
Impact: Data encryption, extortion, potential leaks.
Victim Landscape — Global Reach & Focused Sectors
Regions:
Industries:
Activity Window:
Conclusion
Zarok ransomware exemplifies a new wave of low-cost, high-volume extortionware designed for speed and accessibility rather than precision. Its use of Telegram for negotiation, smaller ransom demands, and a dual threat of encryption and leaks show how modern ransomware operations adapt to exploit victims across different scales. For organizations, early detection, offline backups, and layered email filtering are critical defenses. Individuals should avoid pirated software, maintain OS and antivirus updates, and never engage directly with the attacker’s contact channels. With prompt isolation and professional recovery support, most Zarok incidents can be contained before catastrophic loss occurs.
Frequently Asked Questions
Currently, none exists — stay informed via No More Ransom.
Yes, if clean backups exist or via partial PoC decryption from security professionals.
Phishing attachments, pirated programs, and fake software updates.
Overview: The Menace of RESOR5444 Ransomware RESOR5444 ransomware has emerged as a formidable cyber threat, known for infiltrating computer systems, encrypting vital data, and extorting victims through financial demands. As the sophistication of these attacks continues to rise, the process of retrieving compromised data becomes increasingly complex. This comprehensive guide delves into the inner workings…
Inside the LockBit 3.0 Ecosystem LockBit 3.0 Black, the latest iteration of the infamous LockBit ransomware family, continues to evolve in 2025 with precision-engineered encryption and aggressive double-extortion tactics.This newly observed variant appends random 9–10 character extensions such as “.AZrSRytw3” to encrypted files and leaves a ransom note named “AZrSRytw3.README.txt.” Victims report that all local…
Introduction: The Rising Threat of Orion Hackers Ransomware Orion Hackers ransomware, based on the LockBit 3.0 (LockBit Black) ransomware, has become a serious cybersecurity challenge and a severe problem to the common man that has been encrypting essential data of its victims and demanding high ransom in exchange for the access to this data. Making…
Forensic Dissection of the .hamster15 Ransomware Attack: Inside the MedusaLocker Architecture Strategic Intelligence Briefing: The MedusaLocker Evolution The appearance of files appended with the .hamster15 extension (along with iterative variants like .hamster20, .hamster30, and .hamster50) signals an active compromise by a highly aggressive affiliate of the MedusaLocker Ransomware family. Known for its extensive registry manipulation,…
MAGA ransomware has emerged as a significant threat in the cybersecurity landscape, a variant of Dharma Ransomware, infiltrating systems, encrypting vital files, and demanding ransom in exchange for decryption keys. As the frequency and sophistication of these attacks escalate, individuals and organizations are grappling with the daunting task of data recovery. This comprehensive guide provides…
Overview: The Rising Danger of SKUNK Ransomware SKUNK ransomware has emerged as one of the most aggressive strains of malicious software, notorious for infiltrating systems, encrypting critical files, and extorting victims by demanding cryptocurrency payments. As these threats grow in sophistication and reach, retrieving encrypted data poses a significant challenge for individuals and enterprises alike….